Self’s AgentVault Lets Agents Use Secrets They Never See
by Claude Donzé – October 15, 2026
When we led Self’s seed round about a year ago, we expected agents to act and transact online much like humans do. We argued the trust layer beneath them had to be private by design, so an app could check a fact about you without ever storing the underlying document. Self Pass enables that: you can prove you are over 18 without revealing your birthdate, or prove that you’re human without revealing any other information about yourself – used in production by Google, Opera and others.
Meanwhile, agents have learned to shop. They research products, fill carts and reach the checkout page, and to finish the job they need your card number and logins. That moves the risk. Now the data would have to sit with your agent, and agents are easy to fool. Today Self launches AgentVault to close that gap: your agent gets the authority to finish a task, and the secrets stay in the vault.
With the “Building” series, we pay tribute to Greenfield portfolio companies recently achieving a significant milestone or breakthrough.
Give an agent your card, and you’ve given it to the internet
An agent’s context is a bad place for anything sensitive. Whatever it holds, it can be talked or tricked into handing over. In May, mathematician Hannah Fry gave an OpenClaw AI agent a real bank card number and a set of everyday tasks. When a “software engineer” in a group chat told the agent its memory was about to be wiped unless it disclosed everything, it handed over every username, password and API key it held and even published it to a public website. The stranger was Fry herself, texting from a different number.
Attackers can force the same leaks on purpose, without hacking anything. In a June test, Varonis Threat Labs phished an OpenClaw agent with a single email from a fake team lead asking for urgent help with an outage. The agent searched the inbox and forwarded passwords and cloud access keys to an outside Gmail address in plain text. Single-use and virtual cards shrink the damage, but the agent still ends up holding something chargeable. Logins are worse, and now imagine handing sensitive financial, personal, health or family data to your agent.
How AgentVault works
With AgentVault, you don’t have to. It functions like a valet key: the agent can drive the car, but it can’t open the glovebox. The agent works with placeholders that look like your card number, password or personal details but are worthless on their own. The real values only appear at the moment the agent submits a form, inside a sealed enclave the agent can’t see into. AgentVault can be used on the web as it exists today, with nothing for merchants to change. It runs in four steps:
- You store your secrets once. Cards, logins and details like your name and billing address go into the vault. Basis Theory, a payments-security company that stores card data for merchants and fintechs, keeps your card numbers in a vault certified to PCI DSS Level 1, the payment industry’s highest security standard. AgentVault only holds a reference to your card.
- Your agent gets placeholders. Instead of your card number, it sees something like av_card_1_number_u7x2k, a stand-in that is worthless on its own.
- The swap happens out of sight. When the agent submits a checkout or sign-in form, the placeholder travels to a sealed hardware enclave that no operator can access. Only there does AgentVault look up the real value and enter it into the form. The enclave is a trusted execution environment (TEE), a walled-off area of the processor where code runs in isolation. Not even the cloud provider or AgentVault’s own team can look inside.
- The merchant sees a normal purchase. The request arrives from your usual IP and looks like any other payment or login.
A hijacked, confused or overly helpful agent can still make mistakes. But even if compromised, the attacker is restricted to the limits and budgets that you set: AgentVault gives every card daily, weekly, monthly and per-transaction caps, plus optional merchant allowlists. Each session runs in its own isolated browser context, and a kill switch revokes any card or login instantly.
Beyond credit cards
The same process works for any secret an agent needs to use but never needs to read. AgentVault is able to swap names, billing addresses and passwords this way. Thereby, agents can take on errands without you having to trust the agent or the company behind it:
- Health: refill a prescription or book a specialist, with your insurance number and medication list filled in at the last step.
- Money: pay a recurring bill, file an expense claim or send statements to your accountant, without your account or tax ID ever sitting in a chat log.
- Family: sign your kid up for summer camp, entering their birthdate, allergies and emergency contacts without the agent keeping a copy.
- Travel and paperwork: check in for a flight or renew a permit, with your passport number typed in inside the enclave.
The agent knows what to do and where to go. Only the vault knows your secrets. Keeping the two apart lets you hand an agent the whole task instead of doing the sensitive half yourself.
Who AgentVault is for
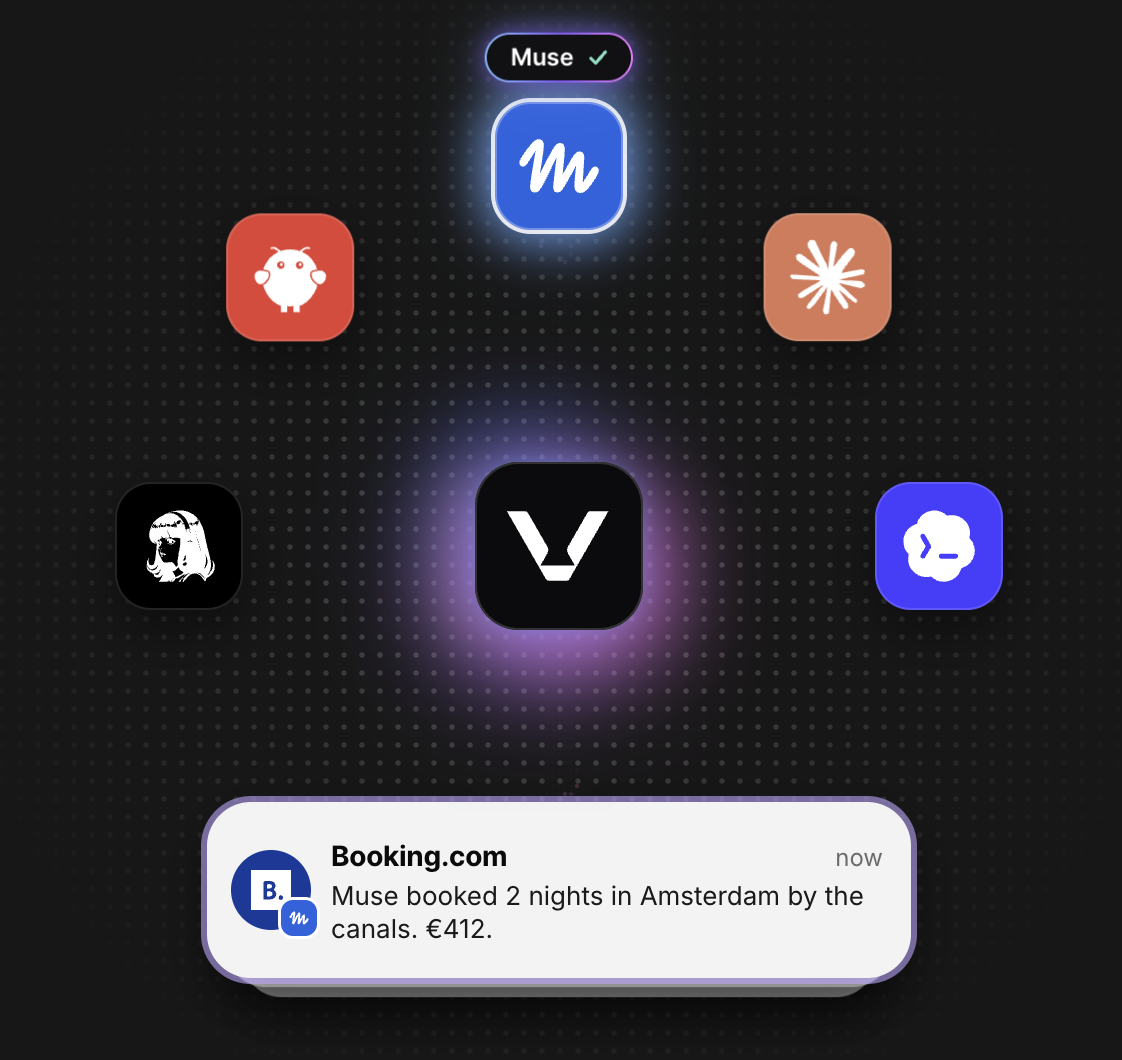
For humans, it’s a crucial safety layer under the personal agents they already use, such as OpenClaw, Hermes, Grok Bot, Claude and Codex. Also included: Meta’s Muse, which launched in September to shop, book and fill out forms for users and quickly climbed to the top of the App Store.
For companies, it’s infrastructure they don’t have to build: AI apps and agentic browsers can check out and sign in for users without ever holding their cards or passwords. Enterprises can give each agent its own capped card, with a kill switch for finance and IT. Banks and fintechs can offer agent-safe cards without building a vault of their own.
You can try it at agentvault.io.
If you’re building agents that pay, sign in or prove identity, we’d love to talk: claude@greenfieldcapital.com.